
Amazon AWS Certified Professional DOP-C02試験情報を紹介します-killtest
AWS DOP-C02試験 は、AWS 認定 DevOps エンジニア - スペシャリティ試験の試験コードです。 AWS Certified Professional資格認定 DevOps エンジニア - スペシャルティ試験の準備をしている場合、killtestは、試験に簡単に合格するために必要なすべての質問と回答を網羅した最新の AWS 認定 DevOps エンジニア - スペシャルティ DOP-C02 ダンプを提供します。 最新かつ正確な情報にアクセスできるように、ダンプは定期的に更新されます。 当社の AWS Certified DevOps Engineer - Specialty DOP-C02 ダンプを使用すると、DevOps の概念と実践をより深く理解し、それらを実際の現場でより適切に実装できます。 killtestの DOP-C02 ダンプを選択して、すぐに AWS 認定 DevOps エンジニア - プロフェッショナルになりましょう!
AWS 認定 DevOps エンジニア – 専門 DOP-C02 ダンプ
AWS 認定 DevOps エンジニア - プロフェッショナル
AWS 認定 DevOps エンジニア - AWS プラットフォームでの分散アプリケーション システムの構成、運用、管理における個人の技術的専門知識を専門的に実証し、同僚、関係者、顧客に対する自信と信頼性を高めます。 これらの資格のある専門家を擁する組織は、安全で準拠性が高く、可用性が高く、スケーラブルなシステムを迅速に提供することができます。
AWS 認定 DevOps エンジニア - スペシャライゼーション (DOP-C02) 試験は、DevOps エンジニアの役割を持つ個人を対象としています。 この試験は、AWS 上の分散システムとサービスの構成、運用、管理における受験者の技術的専門知識を検証するように設計されています。
試験では、受験者の以下の能力も検証されます。
● AWS 上で継続的デリバリー システムと方法論を実装および管理します。
● セキュリティ管理、ガバナンス プロセス、コンプライアンス検証を実装および自動化します。
● AWS 上でモニタリング、メトリクス、ロギング システムを定義してデプロイします。
● 可用性が高く、スケーラブルな自己修復システムを AWS に実装します。
● 運用プロセスを自動化するツールを設計、管理、保守します。
試験の概要
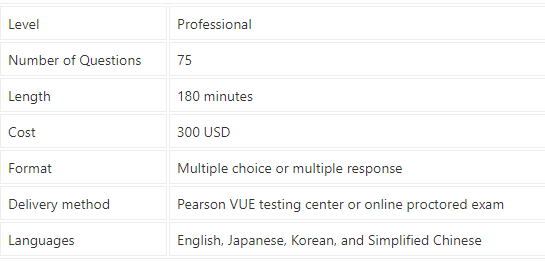
AWS DOP-C02 試験ドメイン
認定資格の目的は、以下のドメインにわたって AWS によって定義されたさまざまな主要分野にわたる知識を検証することです。各ドメインは全体のスコアの合計パーセンテージに寄与します。 これらのドメインは次のように分類されます。
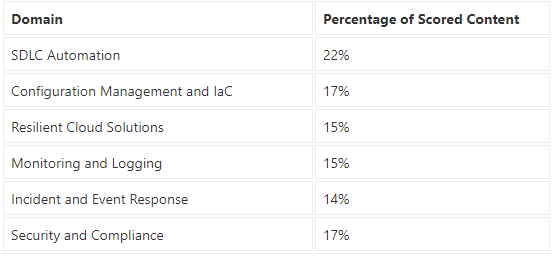
ドメイン 1: SDLC 自動化 (22%)
このドメインでは、コード リポジトリと CI/CD パイプラインを構成してソフトウェア開発ライフサイクルを自動化する必要があります。 これらのパイプラインをさまざまなアプリケーション環境と統合する方法と、自動テストを使用してアプリケーションがデプロイの準備ができていることを確認する方法を理解しておく必要があります。 さらに、アーティファクト リポジトリを作成および構成でき、コンテナまたはサーバーレス アーキテクチャに関連するさまざまなデプロイメント戦略を理解できる必要があります。
ドメイン 2: 構成管理とコードとしてのインフラストラクチャ (17%)
このドメインでコードまたは IaC テンプレートとしてインフラストラクチャを設定およびデプロイするには、AWS CloudFormation、AWS CDK、および AWS SAM を使用する必要があります。 また、複数の AWS リージョンおよびアカウント間で CloudFormation StackSet を使用する方法を完全に理解する必要があります。 さらに、AWS Organizations や Control Tower を使用してアカウントを一元管理する方法など、マルチリージョンおよびマルチアカウント環境のベストプラクティスに精通していることが不可欠です。
大規模な環境全体でタスクを実行できる自動ソリューションを設計、構築、構成するには、Systems Manager、Step Functions、OpsWorks などのサービスを利用する必要があります。
ドメイン 3: 復元力のあるクラウド ソリューション (15%)
このドメインは、堅牢かつスケーラブルで可用性の高いソリューションの実装に重点を置いています。 パフォーマンスと可用性の要件を満たすには、自動スケーリング、負荷分散、およびキャッシュを利用するだけでなく、マルチ AZ およびマルチリージョンの展開を構成する必要があります。 さらに、自動化されたバックアップ、復元、フェイルオーバー プロセスの実装、テスト、構成に熟練している必要があります。 目標復旧時間と目標復旧時点 (RTO/RPO) の概念を理解することも重要です。
ドメイン 4: 監視とロギング (15%)
このドメインでは、アプリケーション ログとメトリックの収集、集計、保存の構成に関する知識がテストされます。 AWS Config、CloudWatch、CloudTrail を使用して、さまざまな環境でさまざまなアクションをアラートおよび自動化するために、SNS、EventBridge イベント、または Lambda を利用するイベント駆動型のアーキテクチャを設計できる必要があります。
ドメイン 5: インシデントおよびイベント対応 (14%)
このドメインは、システム レベルやアプリケーション レベルの障害など、アプリケーションのイベントやインシデントの処理をカバーします。 さまざまなタイプの障害を含むさまざまなイベントに応答して、通知およびアラートのプロセスを設定する方法をよく理解しておく必要があります。 さらに、失敗した展開やプロセスを分析するときは、根本原因分析を実行し、必要な構成変更と修復を行って望ましい状態に復元する方法を知る必要があります。
ドメイン 6: セキュリティとコンプライアンス (17%)
この最後のドメインでは、ID およびアクセス管理、セキュリティおよびアクセス制御、セキュリティ監視および監査ソリューションなどの大規模なセキュリティ ソリューションの実装が必要です。 GuardDuty、Inspector、Config などの AWS のサービスを使用して、セキュリティの脆弱性を特定し、一般的なセキュリティの脅威から保護できる必要があります。
AWS DOP-C02 試験の準備のためのヒントは何ですか?
AWS DOP-C02 試験の準備を最大限に整えるために、試験に合格する可能性を高めるのに役立つヒントがいくつかあります。 最も重要なヒントをいくつか紹介します。
1. 試験ガイドを徹底的に確認します。AWS DOP-C02 試験ガイドには、試験の内容、構造、目的の概要が記載されています。 これは、学習中に集中する必要があるトピックやスキルを特定するのに役立つ重要なリソースです。
2. AWS のサービスを使用して実践的な経験を得る: AWS DOP-C02 試験で成功するには、実践的な経験が鍵となります。 さまざまな AWS のサービスと機能を試して、それらがどのように機能するか、また現実の問題を解決するためにどのように使用できるかをより深く理解することが重要です。
3. ホワイトペーパーとドキュメントを確認する: AWS は、クラウド コンピューティング、DevOps、セキュリティに関する幅広いトピックをカバーする豊富なドキュメントとホワイトペーパーを提供しています。 これらのリソースを確認すると、試験で取り上げられる概念とベスト プラクティスをより深く理解できるようになります。
4. 模擬試験を受ける: 模擬試験を受けると、自分の長所と短所を特定し、試験問題の構成について理解を深めることができます。 AWS では、実際の試験体験をシミュレートするように設計された模擬試験をいくつか提供しています。
5. トレーニングコースに参加する: AWS では、DOP-C02 試験の準備に役立つように設計されたいくつかのトレーニングコースを提供しています。 これらのコースは幅広いトピックをカバーしており、AWS ベースのソリューションの導入と管理において実際の経験を持つ AWS 専門家によって教えられます。
AWS Certified DevOps Engineer – Professional DOP-C02 サンプル質問を見る
1. A company runs an application on one Amazon EC2 instance. Application metadata is stored in Amazon S3 and must be retrieved if the instance is restarted. The instance must restart or relaunch automatically if the instance becomes unresponsive.
Which solution will meet these requirements?
A. Create an Amazon CloudWatch alarm for the StatusCheckFailed metric. Use the recover action to stop and start the instance. Use an S3 event notification to push the metadata to the instance when the instance is back up and running.
B. Configure AWS OpsWorks, and use the auto healing feature to stop and start the instance. Use a lifecycle event in OpsWorks to pull the metadata from Amazon S3 and update it on the instance.
C. Use EC2 Auto Recovery to automatically stop and start the instance in case of a failure. Use an S3 event notification to push the metadata to the instance when the instance is back up and running.
D. Use AWS CloudFormation to create an EC2 instance that includes the UserData property for the EC2 resource. Add a command in UserData to retrieve the application metadata from Amazon S3.
Answer: B
2. A company wants to use AWS CloudFormation for infrastructure deployment. The company has strict tagging and resource requirements and wants to limit the deployment to two Regions. Developers will need to deploy multiple versions of the same application.
Which solution ensures resources are deployed in accordance with company policy?
A. Create AWS Trusted Advisor checks to find and remediate unapproved CloudFormation StackSets.
B. Create a Cloud Formation drift detection operation to find and remediate unapproved CloudFormation StackSets.
C. Create CloudFormation StackSets with approved CloudFormation templates.
D. Create AWS Service Catalog products with approved CloudFormation templates.
Answer: D
3. A DevOps engineer at a company is supporting an AWS environment in which all users use AWS IAM Identity Center (AWS Single Sign-On). The company wants to immediately disable credentials of any new IAM user and wants the security team to receive a notification.
Which combination of steps should the DevOps engineer take to meet these requirements? (Choose three.)
A. Create an Amazon EventBridge rule that reacts to an IAM CreateUser API call in AWS CloudTrail.
B. Create an Amazon EventBridge rule that reacts to an IAM GetLoginProfile API call in AWS CloudTrail.
C. Create an AWS Lambda function that is a target of the EventBridge rule. Configure the Lambda function to disable any access keys and delete the login profiles that are associated with the IAM user.
D. Create an AWS Lambda function that is a target of the EventBridge rule. Configure the Lambda function to delete the login profiles that are associated with the IAM user.
E. Create an Amazon Simple Notification Service (Amazon SNS) topic that is a target of the EventBridge rule. Subscribe the security team's group email address to the topic.
F. Create an Amazon Simple Queue Service (Amazon SQS) queue that is a target of the Lambda function. Subscribe the security team's group email address to the queue.
Answer: A,C,E
4. A DevOps engineer needs to back up sensitive Amazon S3 objects that are stored within an S3 bucket with a private bucket policy using S3 cross-Region replication functionality. The objects need to be copied to a target bucket in a different AWS Region and account.
Which combination of actions should be performed to enable this replication? (Choose three.)
A. Create a replication IAM role in the source account
B. Create a replication I AM role in the target account.
C. Add statements to the source bucket policy allowing the replication IAM role to replicate objects.
D. Add statements to the target bucket policy allowing the replication IAM role to replicate objects.
E. Create a replication rule in the source bucket to enable the replication.
F. Create a replication rule in the target bucket to enable the replication.
Answer: A,D,E
5. A company runs an application with an Amazon EC2 and on-premises configuration. A DevOps engineer needs to standardize patching across both environments. Company policy dictates that patching only happens during non-business hours.
Which combination of actions will meet these requirements? (Choose three.)
A. Add the physical machines into AWS Systems Manager using Systems Manager Hybrid Activations.
B. Attach an IAM role to the EC2 instances, allowing them to be managed by AWS Systems Manager.
C. Create IAM access keys for the on-premises machines to interact with AWS Systems Manager.
D. Run an AWS Systems Manager Automation document to patch the systems every hour.
E. Use Amazon EventBridge scheduled events to schedule a patch window.
F. Use AWS Systems Manager Maintenance Windows to schedule a patch window.
Answer: A,B,F
 認証
 お支払方法
 お問い合わせ
 安全なお支払い


